
SECURITY FOR THE OFFENSIVE AI ERA
AI attacks take minutes. Your backlog takes months. RedRok takes the path away.
RedRok's AI agents see your estate the way an AI attacker does: from outside, inside and the dark web. They prove which attack paths are real and name the few choke-point fixes that remove the risk, continuously and safely.
MANAGED CTEM FOR SERVICE PROVIDERS
Your clients face AI attackers. You can't staff for every one. RedRok scales you to all of them.
Deliver managed CTEM to every client from one multi-tenant cockpit, white label and consumption billed. Live per client in under five days, agentless.
TRUSTED BY SECURITY & ENGINEERING TEAMS AT
- IT-Guru
-
 Team Netcom
-
 Sheba Medical Center
-
 eTeacher Group
-
 ADAMA
-
 HaPool
-
 Masav
-
 Danyel Biotech
- Israel Tax Authority
-
 Cybrella
-
 TerminalX
- The Rabbinical Courts
-
 Armata
-
 BBalev
-
 Ambar Feed Mill
- Enforcement Authority
-
 Maytronics
-
 PowerCard
-
 CyberAntix
-
 Global Performance
- IT-C
-
 Topico
THE PROOF
One chain your ten tools could not see
Illustrative chain KC-0417: contractor VPN to DB-Prod-Master, 10 hops, 98% reproducible.
Every asset, identity and route is a node. Every reachable action is an edge. RedRok walks the graph the way an attacker does, not the severity queue.
-
Attacker
- 01
internet scan
VPN-PORTAL-EXT
- 02
valid login, no MFA
Contractor credential
- 03
VPN lands inside
Contractor VLAN
- 04
route enumeration
Route to servers
- 05
flat L2, no ACL
RDP token on FS-02
- 06
RDP to the jump host
JumpHost-01 CHOKE
- 07
jump host reaches app tier
APP-SRV-04
- 08
pre-auth RCE runs as svc
svc_appsrv
- 09
unconstrained delegation
AD-01 CHOKE
- 10
DCSync, then read replica
DB-Prod-Master
- host
- identity
- network path
- data store
- choke point
- LOW
- MEDIUM
- HIGH
- CRITICAL
Five of the nine exposures are Low or Medium alone. Five tools each saw one node. No tool saw the path.
A MULTI-TYPE ATTACK GRAPH
Breaches don't run on CVEs alone.
Most successful breaches chain different weaknesses. RedRok builds one graph from every type an attacker exploits, then finds the path that links them.
65%
of initial access is identity based, not a CVE
Unit 42, 2026
-
CVEs
Exploitable vulnerabilities on reachable hosts, validated in context.
VULN SCANNER SEES THIS
-
Credentials, stolen or cached
Infostealer leaks, dumped passwords and cached admin tokens.
THREAT INTEL OR EDR SEES THIS
-
Exposed services
Internet-facing panels, VPN portals and forgotten assets.
ATTACK SURFACE TOOL SEES THIS
-
Open services (RDP, SMB)
Remote access and file services reachable across segments.
NETWORK AUDIT SEES THIS
-
Service accounts
Over-privileged, never-rotated accounts that apps run as.
IDENTITY POSTURE SEES THIS
-
Domain misconfiguration
Unconstrained delegation, DCSync rights, weak tiering.
NO TOOL OWNS THIS
Single-type tools each see one node. RedRok links every type into one path.
See the platformRedRok is for security teams drowning in findings and fighting attackers that never sleep.
-
72 min
Fastest observed time from initial access to confirmed data exfiltration
Unit 42, 2026 Global IR Report
-
3%
of open findings sit on a path an attacker can actually walk
RedRok mission data, mid-sized estate
-
3 fixes
broke 9 of 11 proven chains to crown jewels in one sprint
RedRok customer outcome
THE BACKLOG
41,000 findings. 3% are reachable. Which ones?
Scanners sort by severity, not reachability. Teams patch what is loudest while the exposures that carry real risk survive quarter after quarter.
BEFORE · THE BACKLOG MODEL
41,000
open findings sorted by severity. About 400 closed a quarter. Risk stays flat.
◆ LEAST EFFORT TO BREAK THE CHAINS
3 fixes
break 9 of 11 chains that reach a crown jewel. Risk actually drops.
BOARD QUESTIONS
The questions your board will ask next.
Answered from live mission data, with the trend, not a snapshot.
Explore the platform reporting view. A downloadable sample executive report is coming soon.
-
How much of our critical assets are exposed now vs. last month?
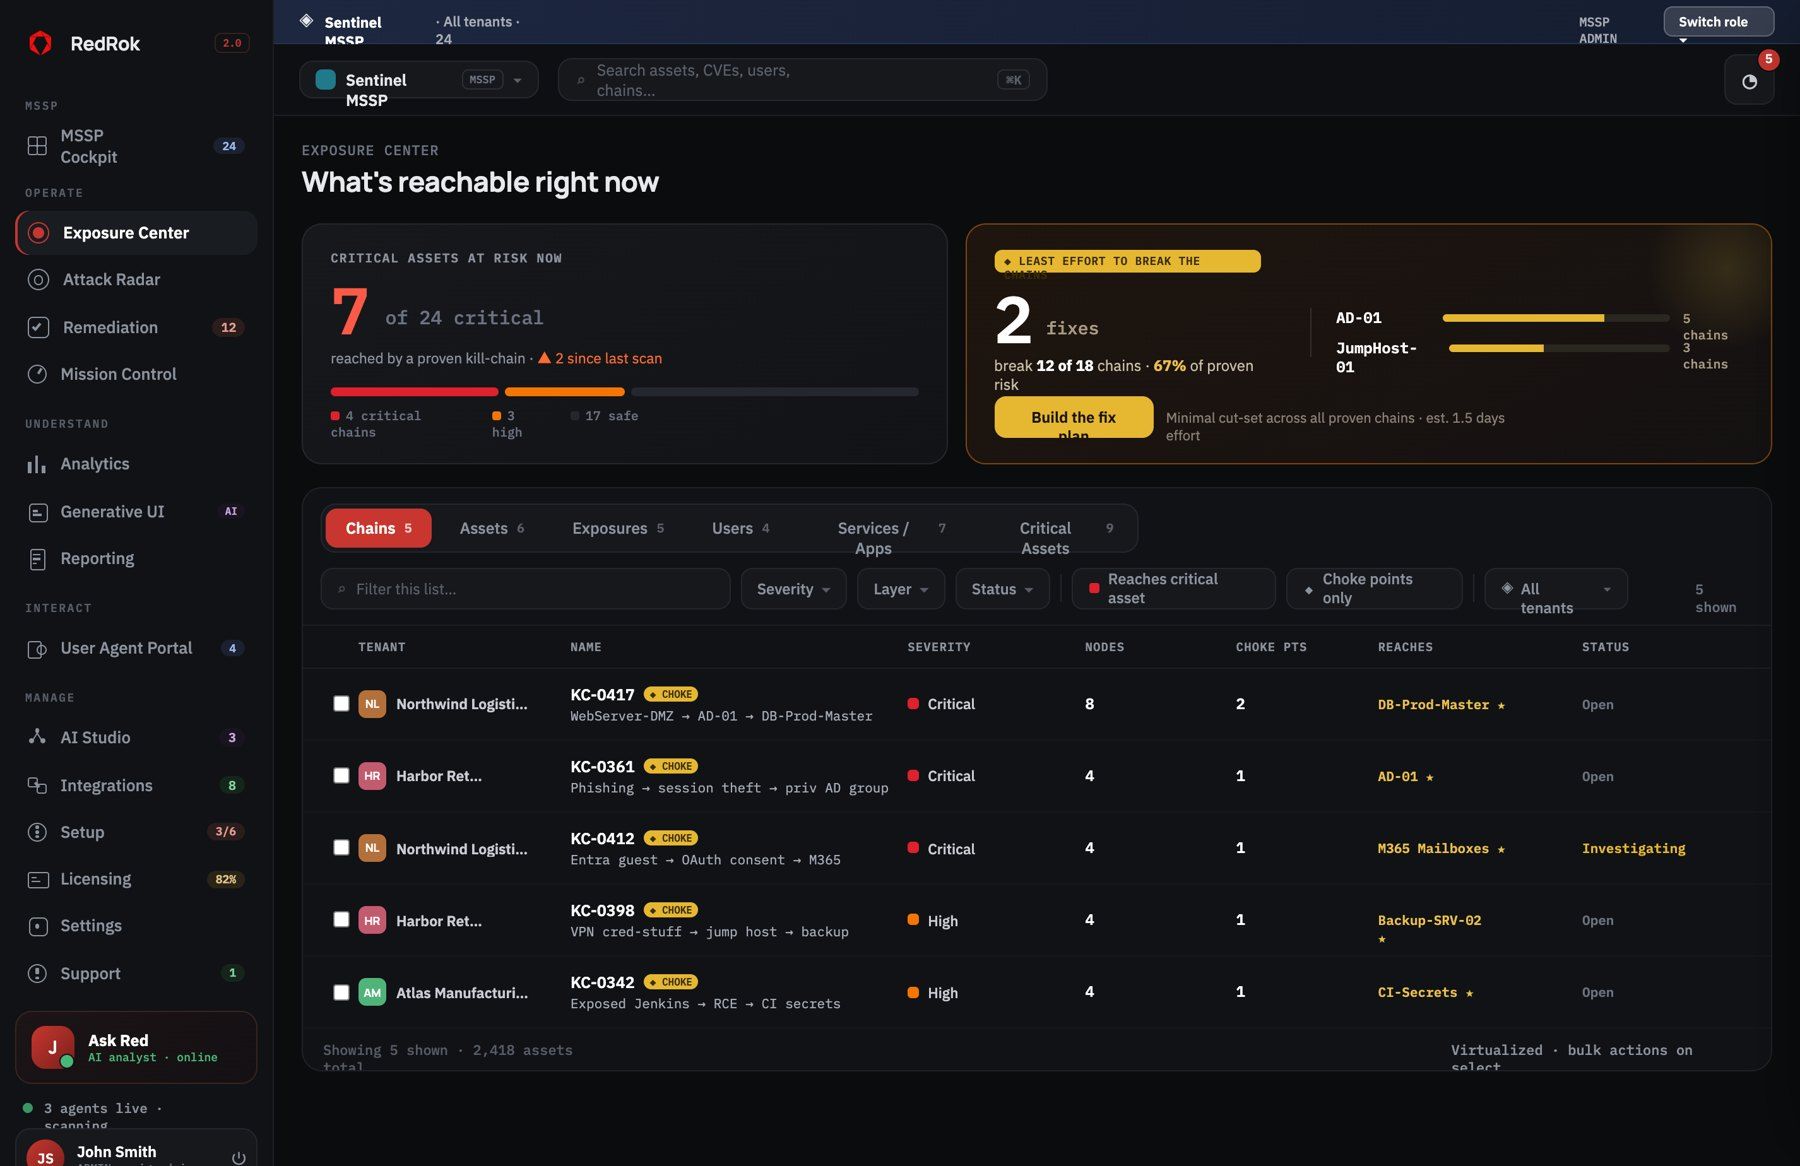
7 of 24
crown jewels reachable
▼ 4 from 11EXPOSURE CENTER 6 MONTHS
-
Has our risk improved or deteriorated?
63
posture score · board target 70
▲ 16 since baselineANALYTICS CENTER 6 MONTHS
-
What moved the number, and what's next?
3 fixes
cut 10 chains this month
Next sprint: 2 fixes, +9 ptsREMEDIATION CENTER 6 MONTHS
-
Are we exposed to what's in the news?
0 paths
from the new critical CVE to a crown jewel
2 of 14 leaked creds still validREDPOOL · ATTACK PATH AGENT 6 MONTHS
Illustrative demo tenant. Values update every mission run.
-
Multi-tenant
from day one, isolated data per client
-
White label
console and reports under your brand
-
Consumption
billing that matches how you sell
-
< 5 days
to onboard a client, agentless
01 MSSP COCKPIT
Your whole portfolio on one screen.
See every tenant ranked by risk, drill into any client and come straight back. Fleet CTEM missions run across tenants from the same screen.
- Average posture, critical assets at risk and SLA breaches across tenants
- Fleet CTEM missions across all tenants or a chosen set
- Ask Red flags your weakest tenant and the one fleet fix that helps most
02 MISSION CONTROL
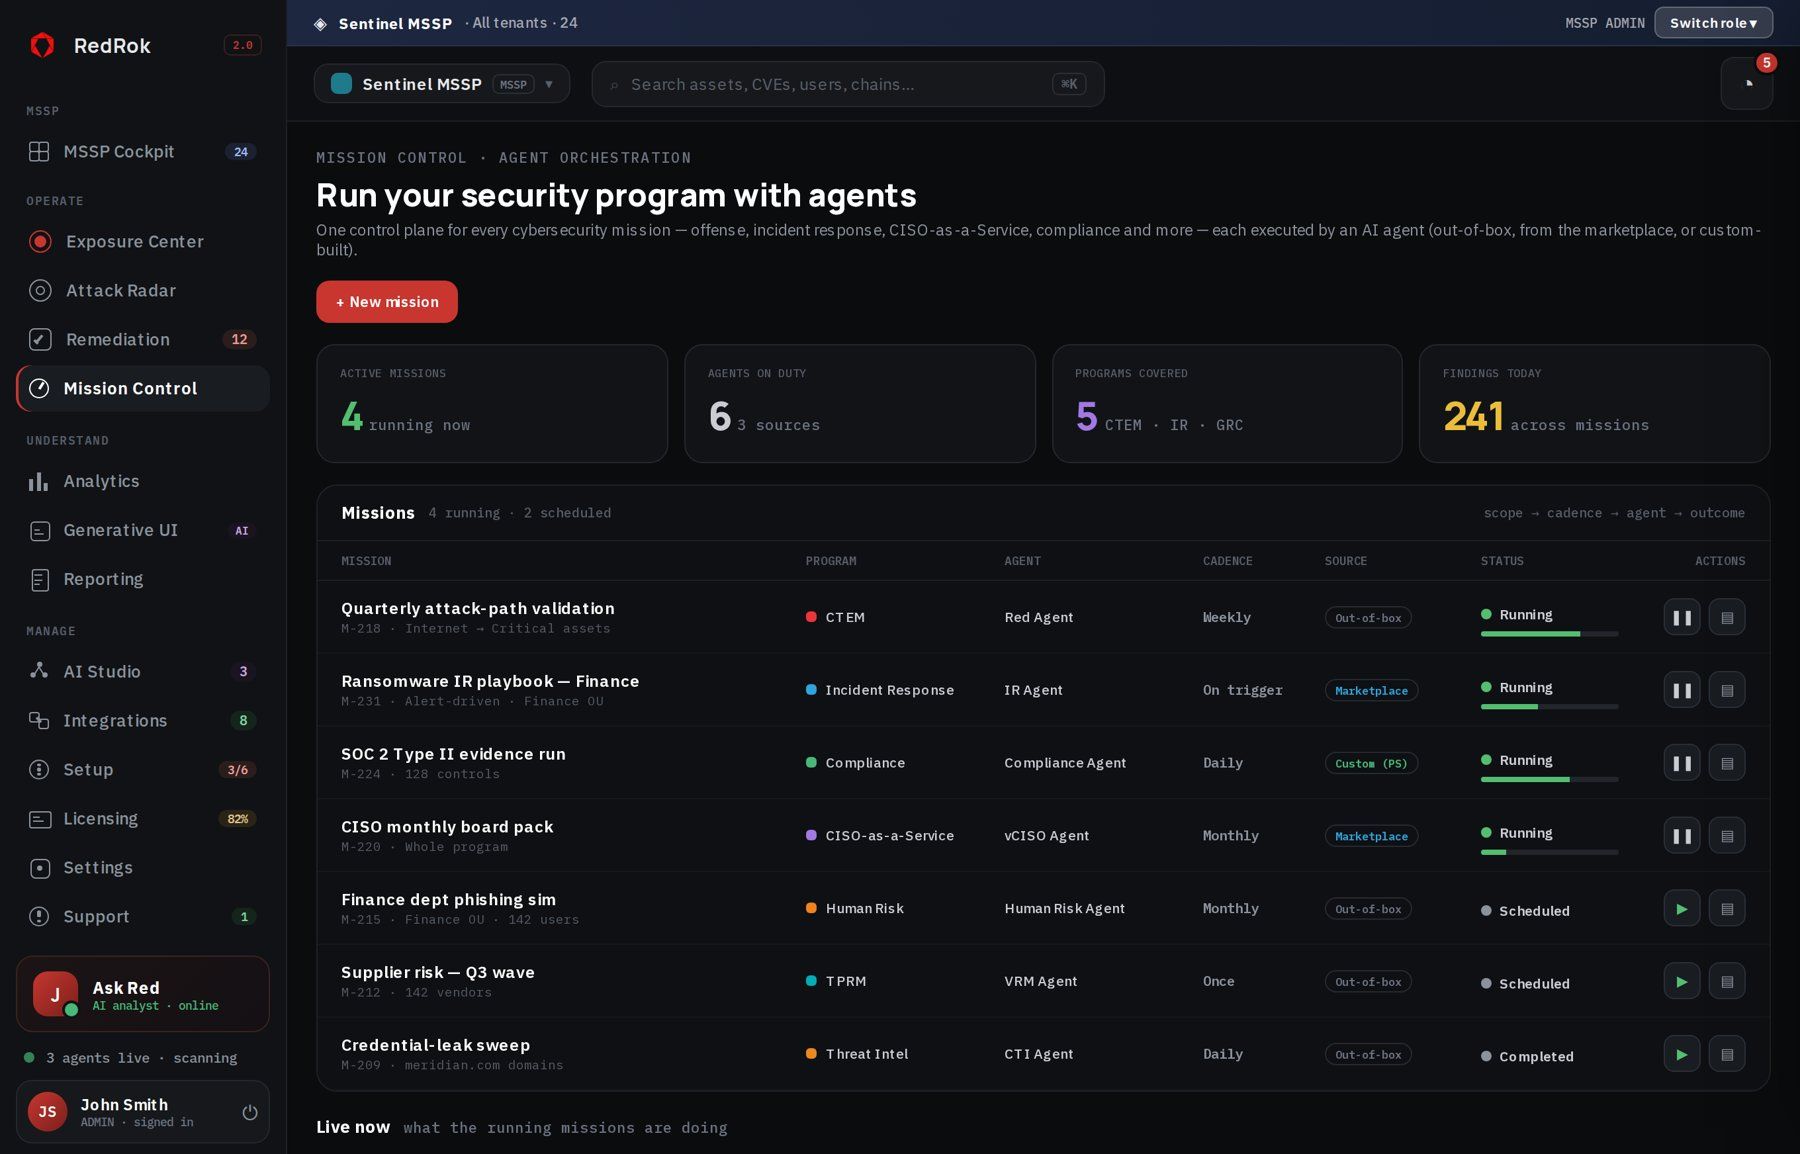
One mission, every client.
Plan, execute and deliver CTEM missions across all tenants or a chosen set, run by RedRok's four agents. As new agents arrive from RedRok, the marketplace or your own team, the same console runs their missions.
- Today: CTEM missions with the External, Internal, CTI and Attack Path agents
- On the roadmap: incident response, compliance, vCISO, TPRM and human-risk missions as new agents ship
- Cadence you set: daily, weekly, monthly, on trigger
- Every mission scoped, scheduled and auditable
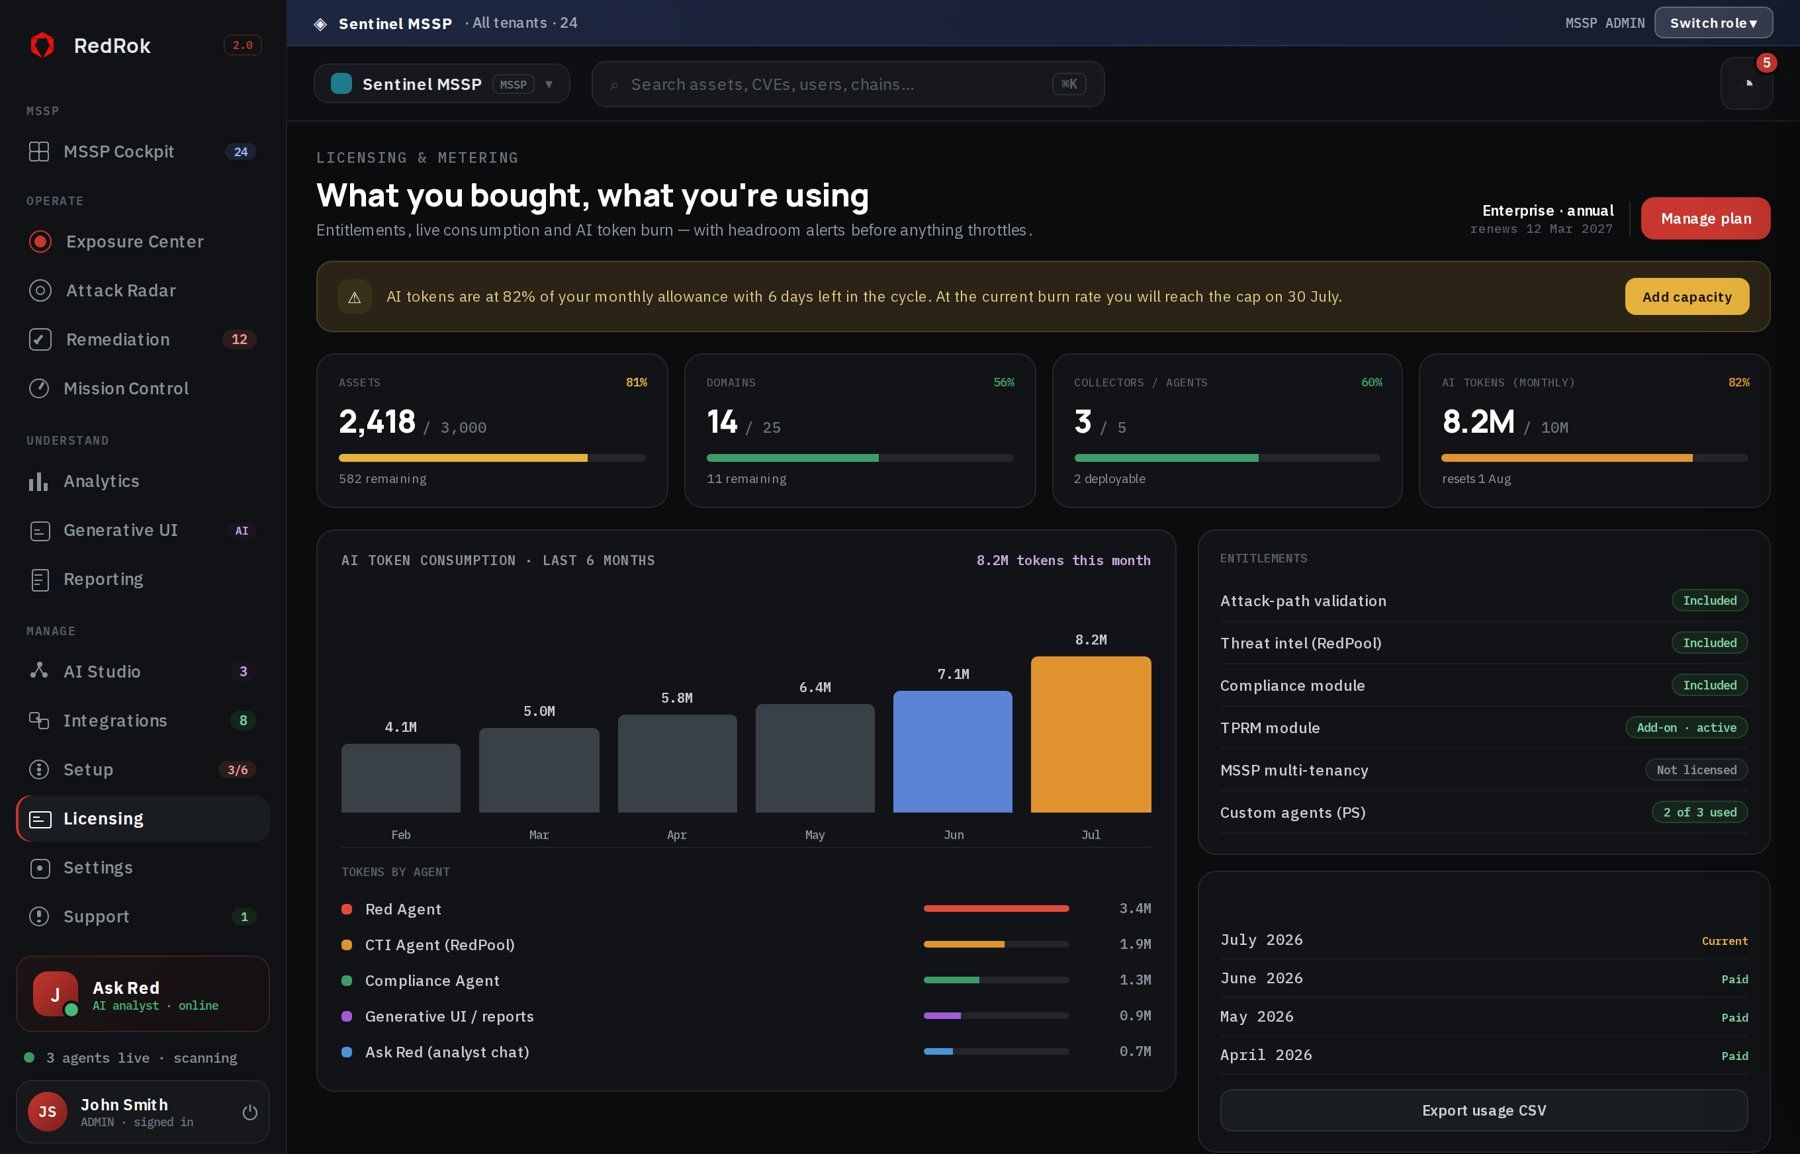
03 LICENSING AND METERING
Know what you bought and what you use.
Entitlements, live consumption and AI token burn per agent, with headroom alerts before anything throttles.
- Assets, domains, collectors and AI tokens against entitlement
- Token consumption by agent over six months
- Usage records exportable to CSV per tenant
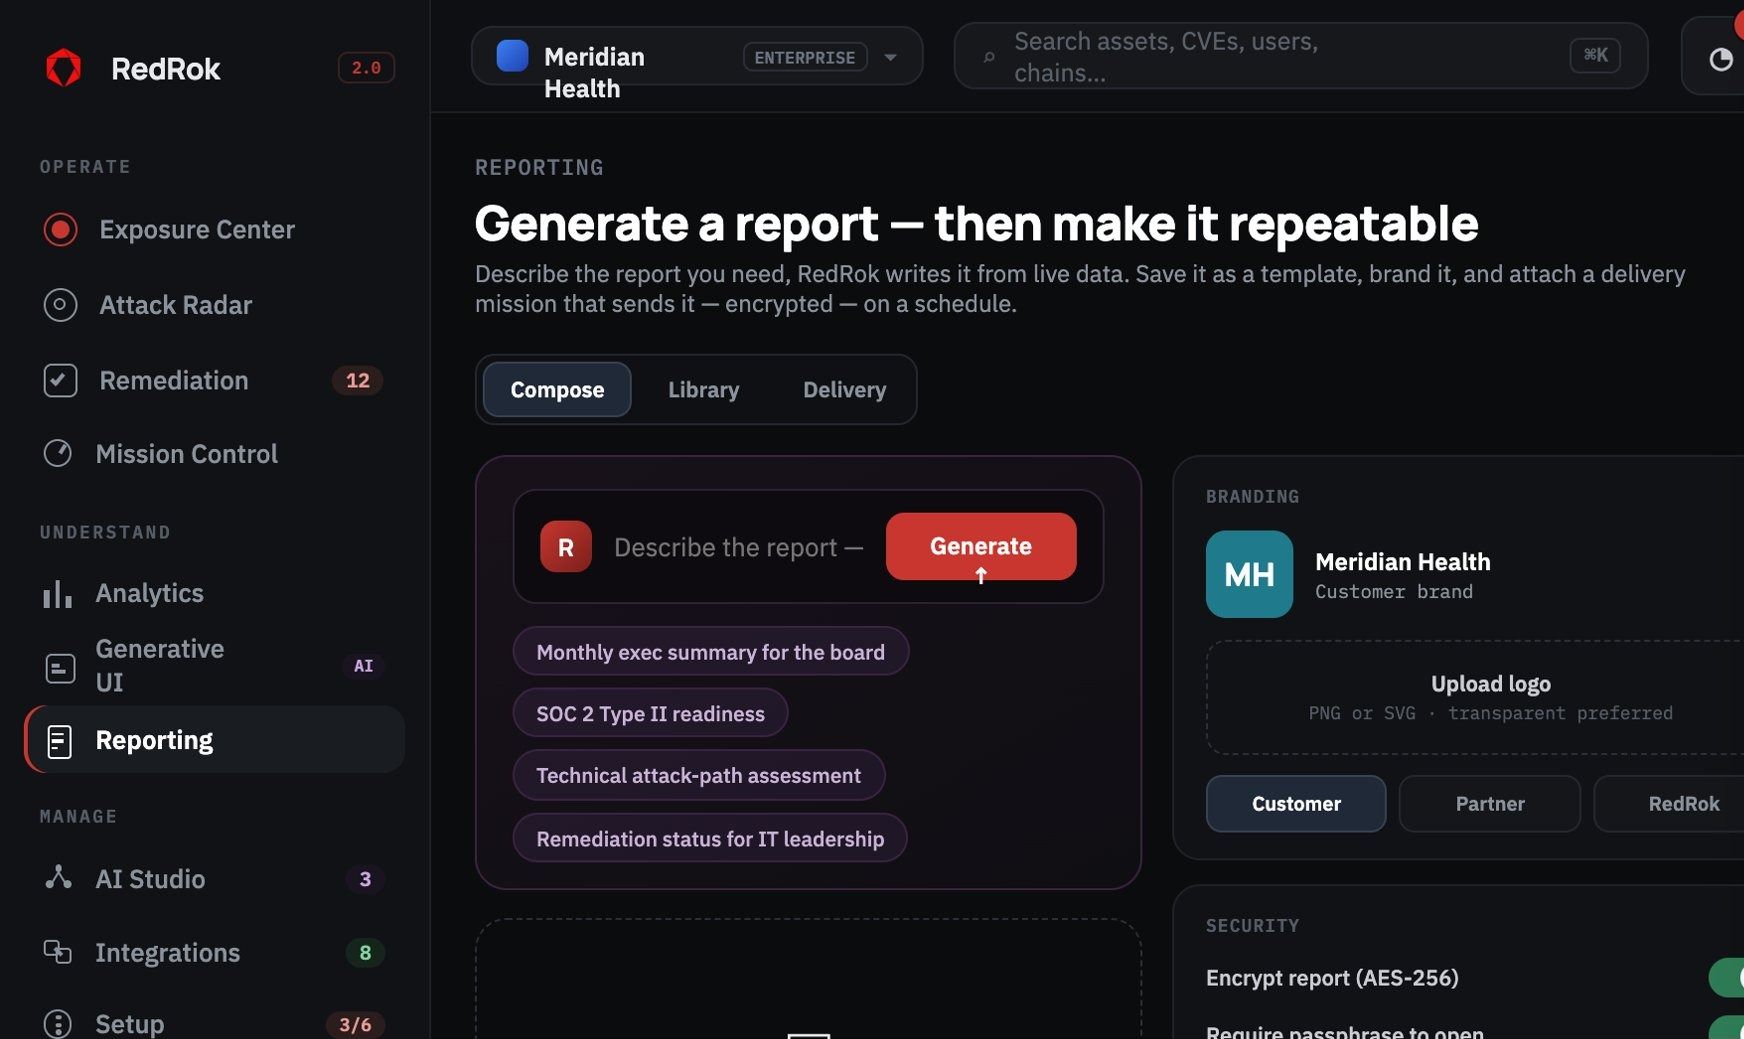
04 WHITE-LABEL REPORTING
Board reports in your client brand.
Generate reports from live mission data, branded per client or as your own service, delivered encrypted on a schedule.
- Customer, partner or RedRok branding per report
- Monthly executive summaries and SOC 2 readiness packs
- One-time links with out-of-band passphrase
SERVICES YOU CAN SELL
Three managed CTEM offers, ready to package.
| OFFER | AGENTS | CLIENT DELIVERABLE |
|---|---|---|
| Exposure Watch | External · CTI (RedPool) | Monthly external surface and leaked-credential report |
| Managed CTEM | All four agents | Proven attack paths, ranked choke-point fixes, monthly board posture report |
| Managed CTEM plus Remediation | All four agents plus your services | Everything above, with your team closing the fixes and proving the score moved |
Launch your managed CTEM service this quarter.
A partner demo of the cockpit with sample tenants, then your first client live in under 5 days.
See your first proven attack path in under an hour.
30-minute demo, then a scoped pilot on one business unit. We reply within one business day to set a time.